#data breach
| gen: 2026/10/30:01:16 in 35.0 sec (old)bias: 5 (Center-Left) |
| type: lolsquality: 56 |
| pts: 0 |
 | author: | Vanessa Romo | institution: | NPR (as displayed) | ¿porque no los dos? |
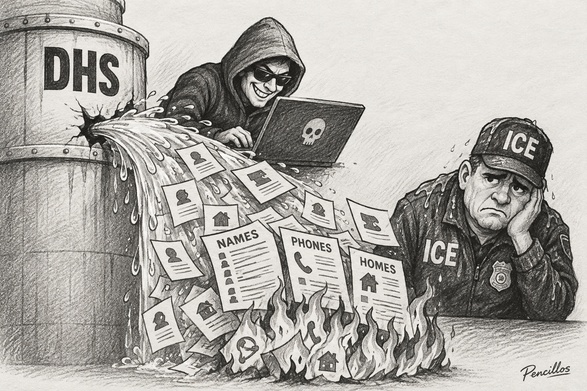
| tl;dr | The article reports that hackers exposed identifying information for more than 40,000 DHS personnel, including undercover staff. It says the stolen records were distributed through searchable databases. Those involved describe the release as supporting government oversight and immigration-enforcement investigations. DHS acknowledges a potential breach and says it is taking protective measures. The article includes agency-level record counts and a correction, but provides little independent verification or analysis of risks to employees. | ||||
| deeper: | The article favors a transparency-and-community-accountability framing, giving leak advocates extensive space while offering only a brief DHS response. This suggests a center-left tilt, though oversight is not exclusively partisan. Strong accusations in quotations go largely unexamined, and employee safety receives little attention. Named sources, numerical context, and a correction improve accountability. However, the definitive headline exceeds DHS’s acknowledgment of a “potential breach,” and “unprecedented” is unsupported. The screenshots alone cannot establish authenticity or verify the reported events. | ||||
media: | |||||
| gen: 2026/09/30:20:54 in 26.6 sec (old)bias: 2 (Center) |
| type: newsquality: 80 |
| pts: 0 |
 | author: | Jenna McLaughlin | institution: | NPR | ¿porque no los dos? |
| tl;dr | The article reports that the FBI is investigating ShinyHunters over stolen sensitive personnel data. Current and former employees describe concerns about inadequate communication and potential exposure of medical, family, and undercover-work information; the FBI says it promptly notified staff. The breach’s scale and entry point remain unclear. The article discusses possible links to vulnerabilities in Oracle’s PeopleSoft software, while distinguishing an earlier Dutch arrest from the current investigation. | ||||
| deeper: | The reporting shows no clear partisan agenda. It balances employee criticism with FBI responses, explains why sources remain anonymous, and distinguishes confirmed information from uncertainties. Links, named expertise, and historical context strengthen the account. However, dramatic language and speculative worst-case consequences heighten alarm. Several important claims depend on unnamed sources, and the PeopleSoft discussion establishes a possibility rather than the actual breach mechanism. The headline is more definitive about responsibility than the opening attribution to the hackers’ claims. | ||||
media: | |||||
You made it to the bottom. Now dance!
owned and operated by: RPN Omnigalactic Insitutution as of: 2026/11/17: 19:28 in 0 ms
Enter Code
Login with Account